Sylvester Eziagor
Information Security Analyst
Safeguarding your digital assets from cyber threats.
About
Hello, I'm Sylvester 👋🏽 an Information Security Analyst with a background in software engineering, giving me a unique perspective on security. Before focusing on cybersecurity, I built enterprise applications, implemented authentication and access controls, and worked closely with infrastructure supporting business-critical systems. That experience taught me an important lesson: even well-designed systems can become vulnerable when people, processes, and technology fall out of alignment.
Today, I help organizations reduce risk through access management, security monitoring, risk assessment, and compliance. My work combines technical analysis with business context, whether I'm investigating incidents, identifying control gaps, reviewing access permissions, or helping ensure systems remain audit-ready. I believe security should enable organizations to operate with confidence—not create unnecessary friction.
I'm passionate about continuous learning and enjoy applying security concepts in hands-on environments. I build detection engineering labs with Splunk, simulate attack scenarios mapped to the MITRE ATT&CK framework, perform enterprise risk assessments using industry standards, and document my findings through technical write-ups and open-source projects.
My background in software engineering allows me to understand how applications are built, while my experience in cybersecurity helps me evaluate how they can be protected. That combination enables me to bridge the gap between development, operations, and security, translating technical findings into practical decisions that support the business.
Experience
June 2025 - present
Compliance Lead · Walmart Canada
Investigate and document workplace and customer incidents from intake to closure, maintaining audit-ready case files and ensuring compliance with regulatory and internal policies. Conduct preliminary reviews, evidence collection, and reporting across safety, ethics, and policy matters, collaborating closely with Asset Protection, HR, and Operations.
Audit
Incident & Event Response
Compliance
Risk Assessment
Safety & Security
July 2022 - December 2024
Support Engineer · Crestflow Energy
Managed Windows-based user access and provisioning through SailPoint, applying role-based permissions and continuous log monitoring to safeguard systems processing payment and metering transactions. Migrated company web applications to in-house infrastructure (cPanel, DNS, Nginx), including SSL hardening, caching, and database query optimization, cutting hosting costs by 20%. Wrote SOPs covering meter vending, tariff configuration, and payment gateway integration.
SailPoint
Windows Server
PowerShell
Vendor Management
Nginx
SSL/TLS
SIEM
2021 - 2024
remote
Backend Developer · PathFinder Idee Tech Solutions
Designed and built backend services and RESTful APIs using Node.js and Express, handling data models, authentication, and business logic for production applications. Collaborated with frontend developers to define API contracts and ensure reliable, well-documented endpoints.
Node.js
Express
TypeScript
PostgreSQL
2019 - 2021
Software Engineer · Zenith Bank Plc
Maintained and enhanced 20+ enterprise banking application modules in Java and Spring Boot, and designed 15+ RESTful APIs for secure integration between internal systems and third-party services. Implemented OAuth2, JWT, and SSO with role-based access control, managed cryptographic keys through the bank's HSM, and applied encryption to sensitive data at rest in Oracle. Optimized existing code and troubleshot production issues to cut average response times by 25%, supported CI/CD and release activities, and authored technical documentation covering architecture, API contracts, and deployment procedures.
Java
Spring Boot
Oracle DB
OAuth2 / JWT
Jenkins
Maven
REST APIs
Projects
Attack Simulation & Detection Engineering
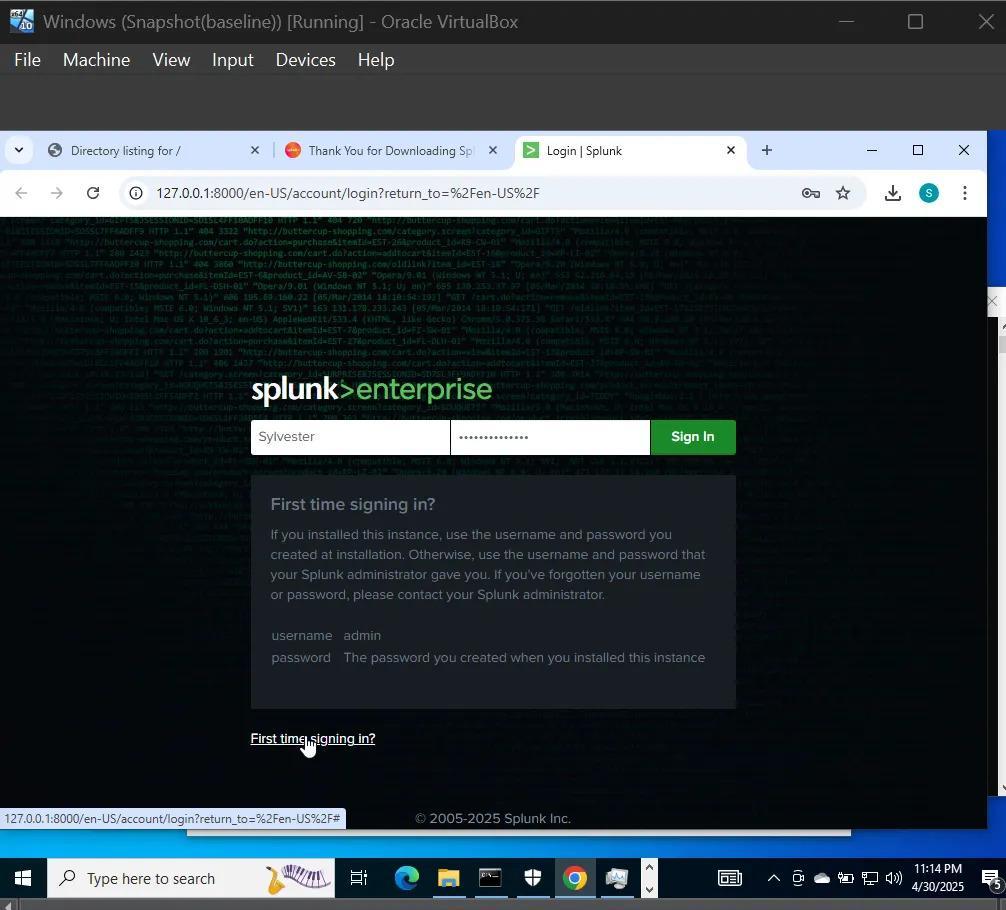
End-to-end purple-team lab: built and delivered a reverse-shell payload from Kali Linux, then switched sides to engineer the detections that catch it. Instrumented the target with Sysmon, shipped logs to Splunk, and wrote detection rules mapped to MITRE ATT&CK covering payload execution, C2 traffic, and Defender tampering — with the full attack-to-detection chain documented in the write-up.
Kali Linux
Splunk
Sigma
Sysmon
MITRE ATT&CK
Reverse Shell
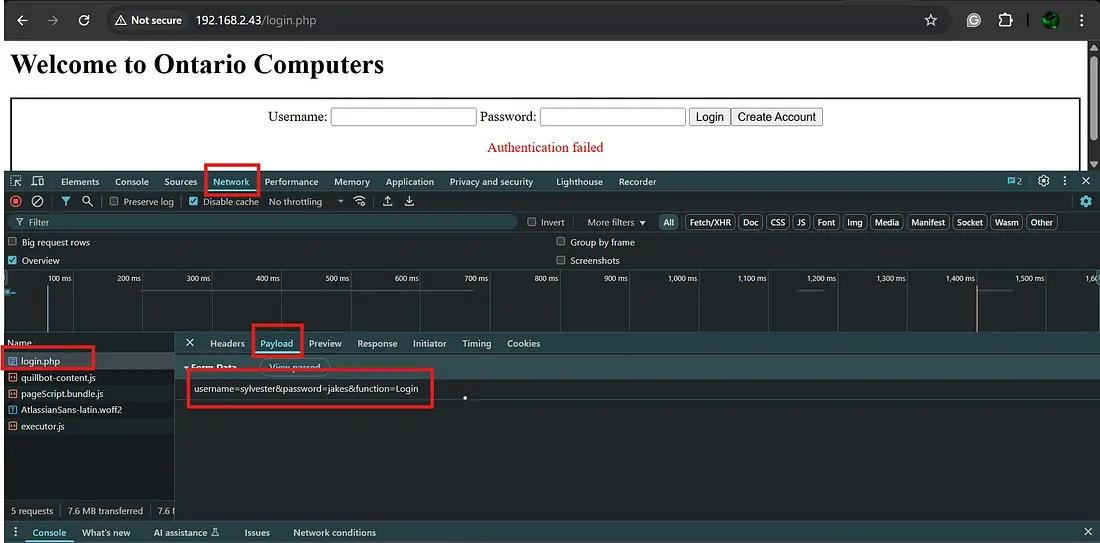
Broken Authentication Lab
Broken authentication lab demonstrating credential stuffing and session hijacking against a deliberately vulnerable PHP login app. Executed credential-stuffing attacks with Postman and a weak-password list, exploited low-entropy session IDs, then authored a defense cheat sheet covering MFA, CAPTCHA, IP intelligence, and headless-browser blocking.
PHP
Postman
OWASP
Credential Stuffing
Session Hijacking
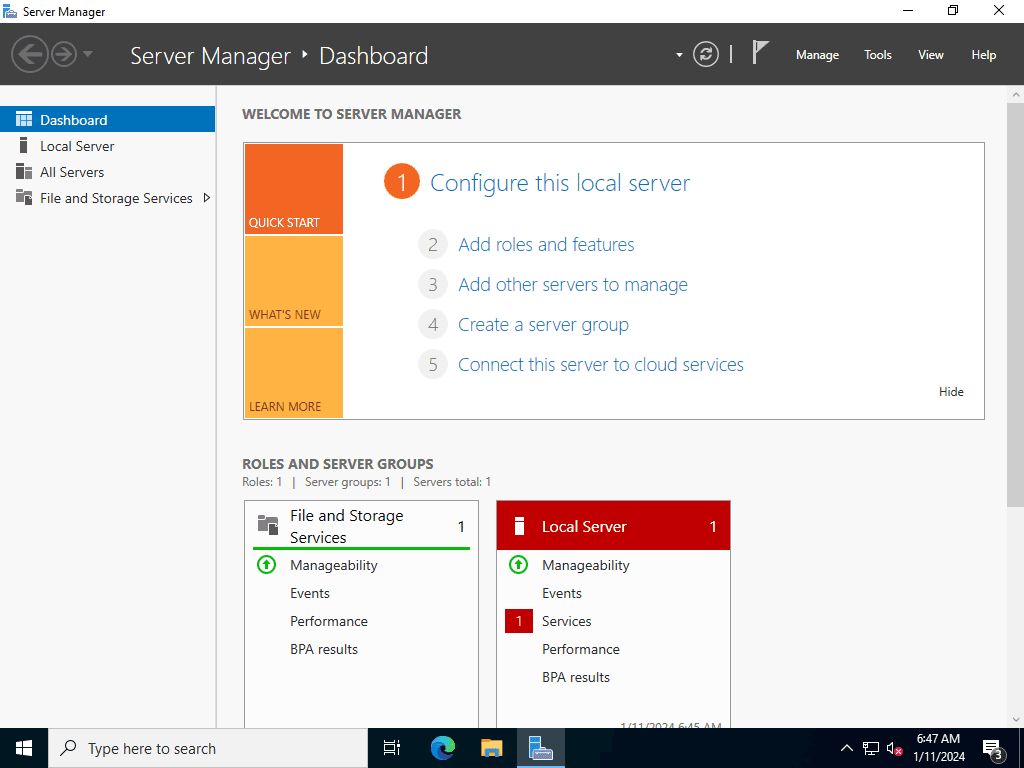
Windows Server AD Lab
Modeled a corporate network in VirtualBox to practice enterprise identity administration: a Windows Server 2019 domain controller running AD DS, DNS, DHCP, and NAT routing via RRAS, plus a domain-joined Windows 10 client. Wrote a PowerShell script to bulk-provision an OU with 1,000 user accounts, then verified authentication, DHCP leases, and connectivity end to end.
Windows Server 2019
Active Directory
DNS/DHCP
PowerShell
RRAS/NAT
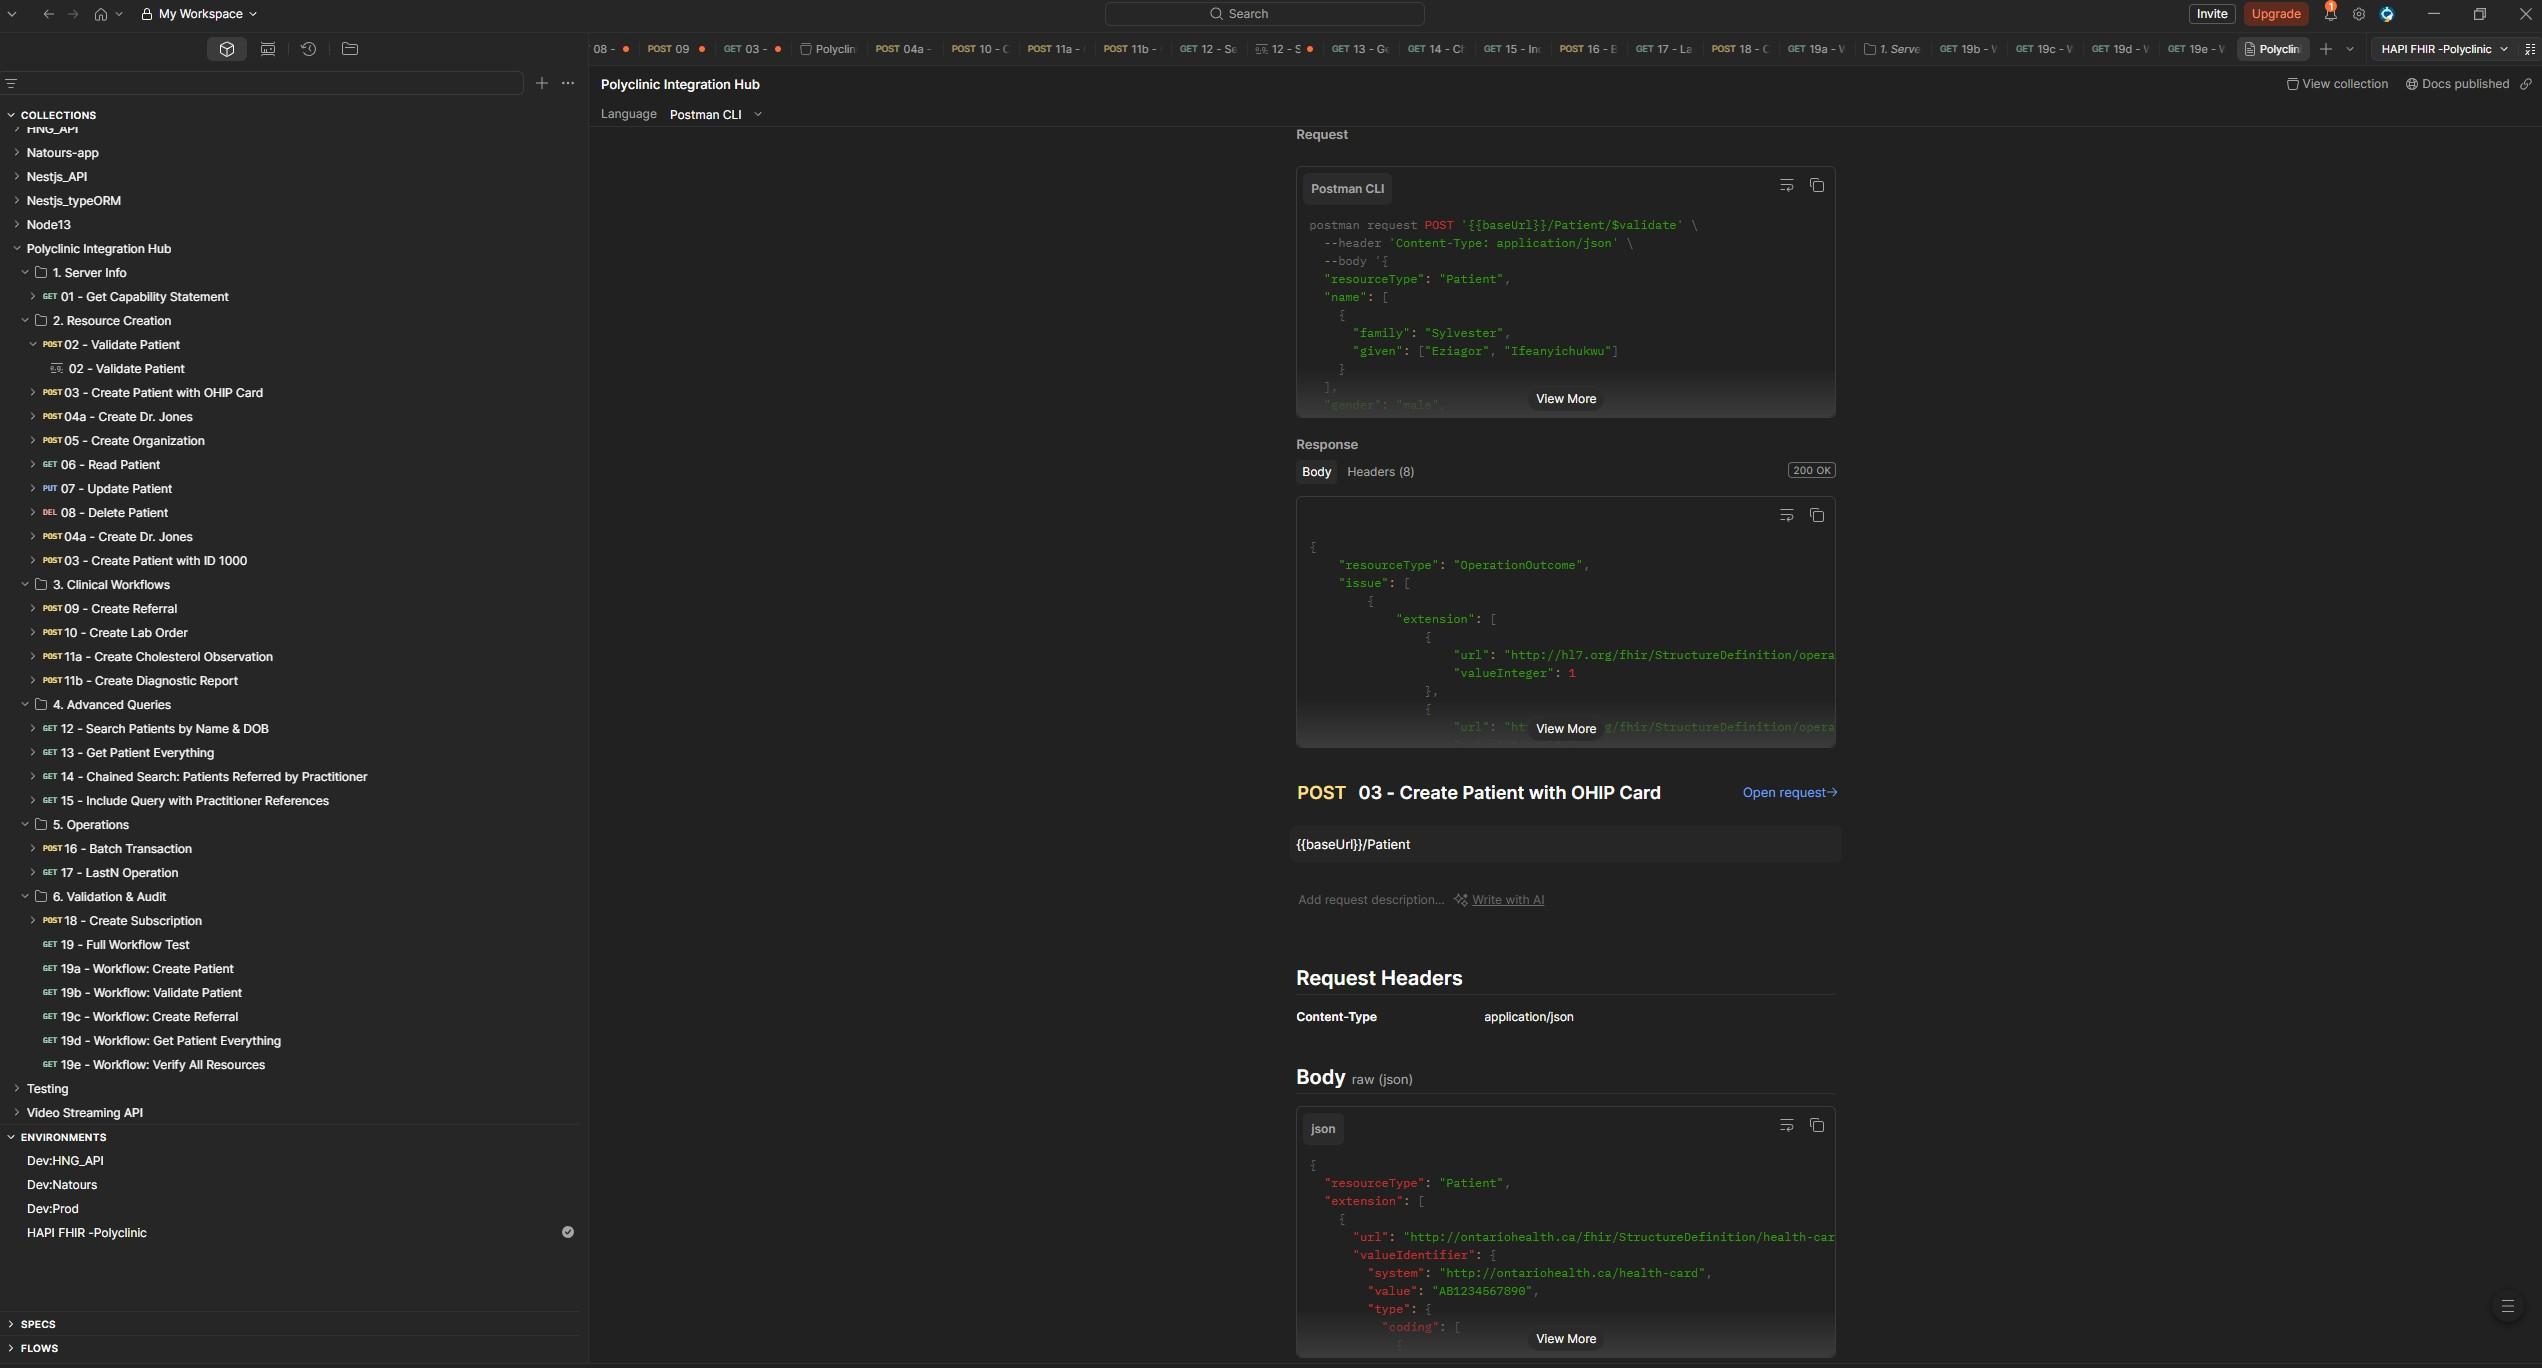
FHIR Polyclinic Interoperability Hub
FHIR R4 server implementation demonstrating healthcare interoperability workflows using HAPI FHIR JPA Server, with RESTful APIs and standards-based data exchange between healthcare systems.
Docker
Postman
Swagger
HAPI FHIR JPA Server
EMR Workflows
Java
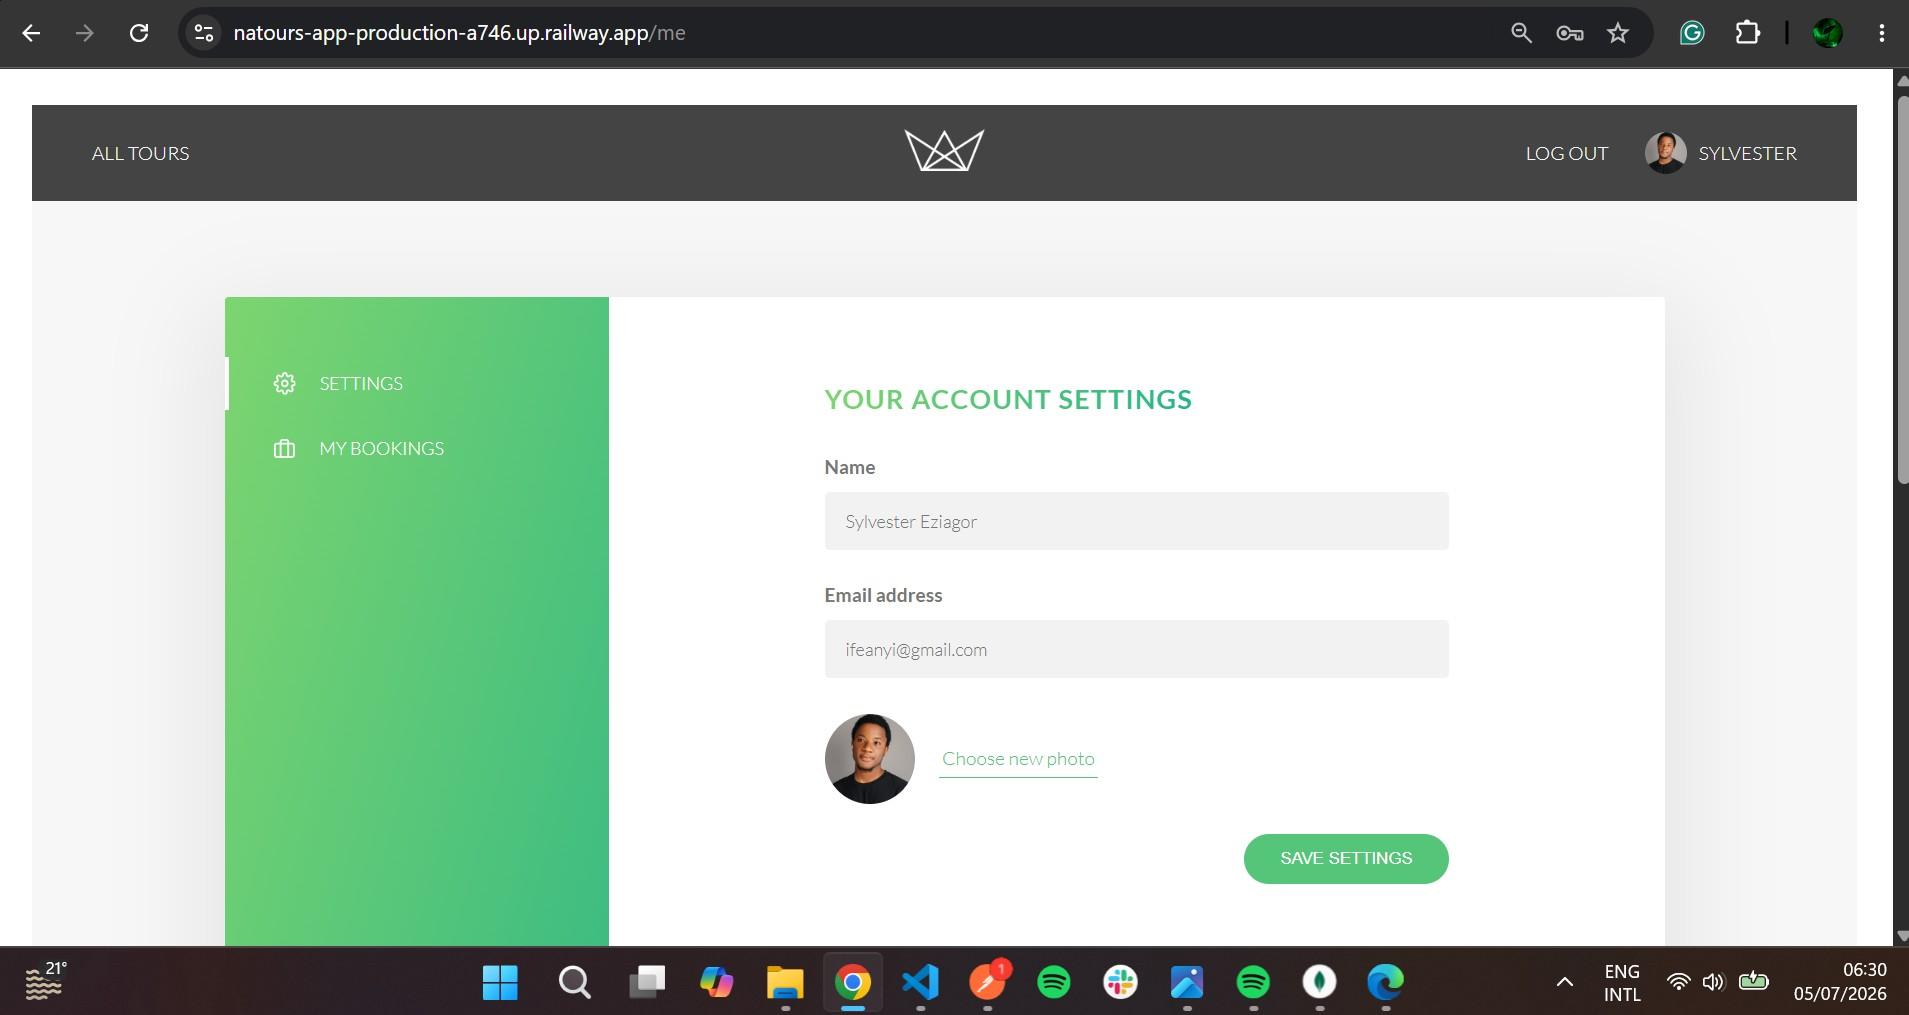
Natours — Tour Booking Platform
A full tour-booking platform built on Node.js, Express, and MongoDB, where security carries the design: stateless JWT auth in httpOnly cookies, bcrypt-hashed passwords, role-based access control, and a hashed, time-limited password-reset flow. Interactive Mapbox tour maps, Paystack payments, and transactional email round out the product.
Node.js
Express
MongoDB
JWT
MapboxGL
Helmet
SendGrid
Paystack
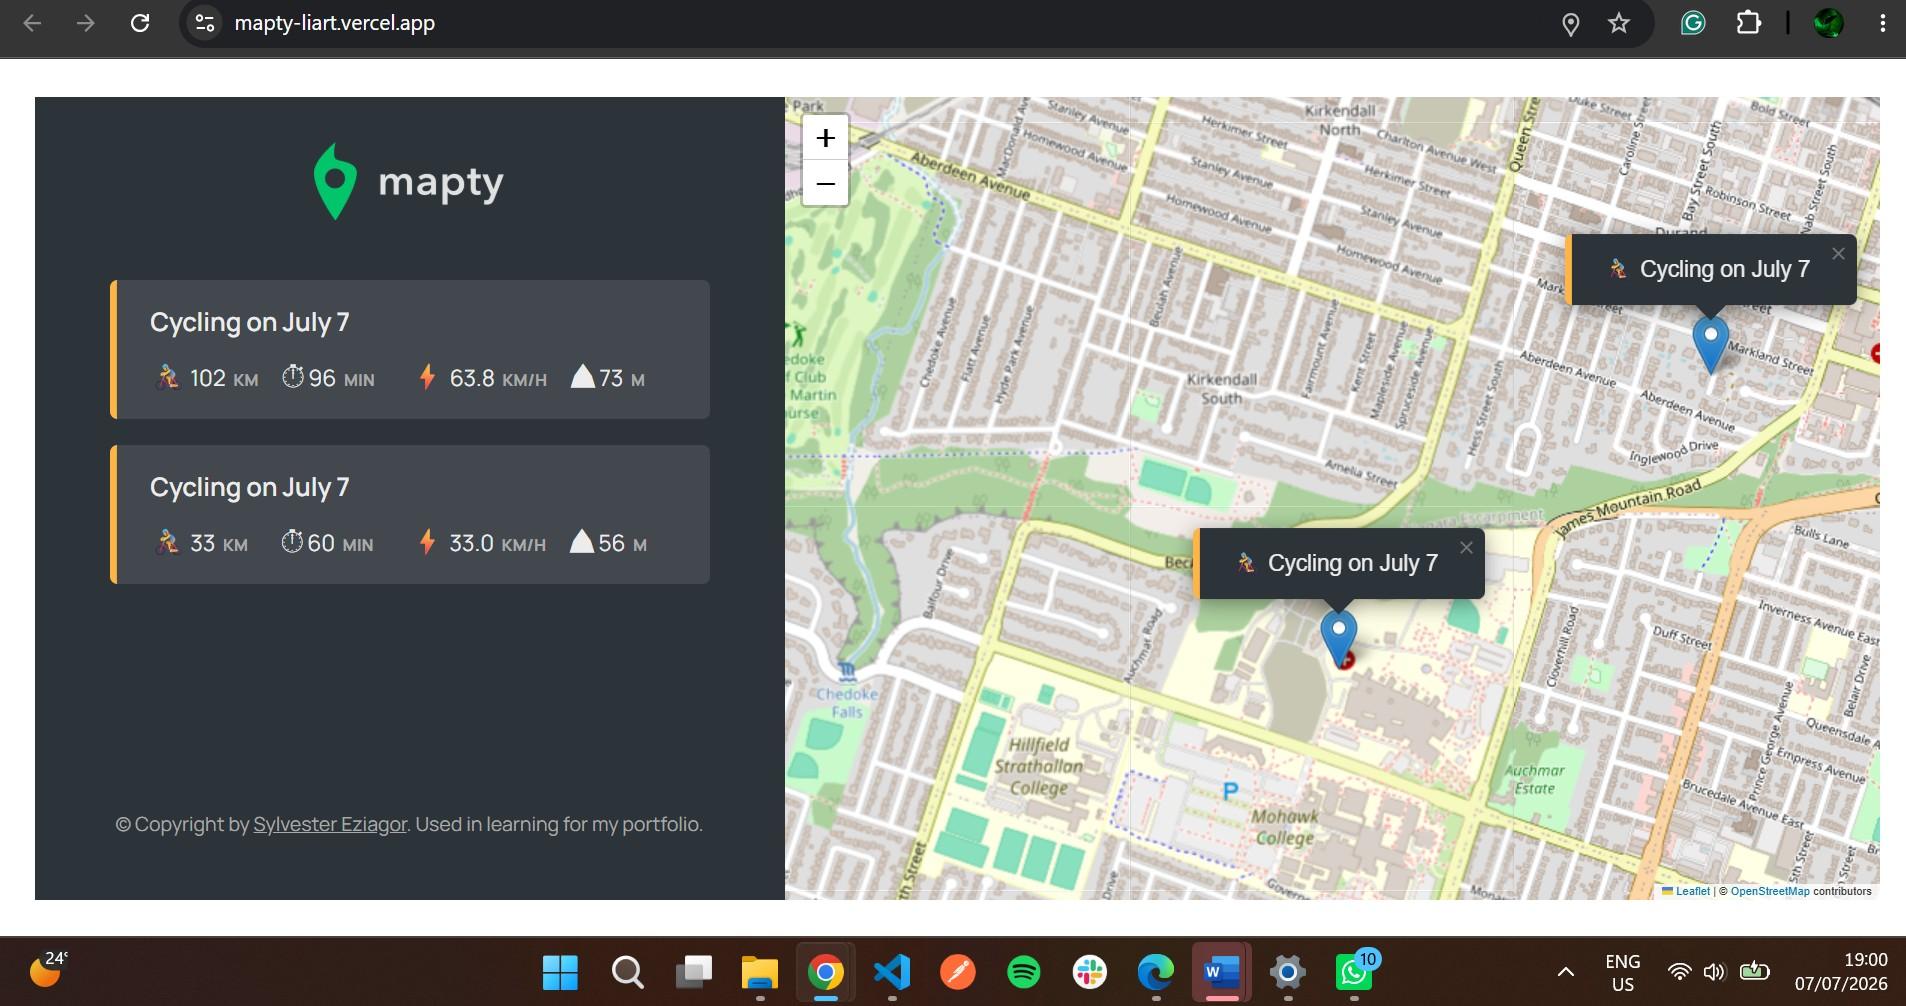
Mapty — Workout Tracker
A workout tracker built in vanilla JavaScript. Click anywhere on the map to log a running or cycling session; it drops a Leaflet marker and adds a card to the sidebar. Uses OOP with a Workout base class and Running/Cycling subclasses, the browser Geolocation API to center the map on your location, input validation, and localStorage that rebuilds workouts as real class instances on reload.
JavaScript
OOP
Leaflet
Geolocation API